Case study · Live2.ai · Enterprise SaaS
Rights Management
Designing a scalable rights management system for UGC at enterprise scale — solving legal, platform and automation constraints without adding headcount.
- Company
- Live2.ai (Woovly India)
- My role
- Head of UX Design
- Users
- Enterprise brand & legal teams
- Focus
- System design · Compliance UX · Automation
Impact
From manual chaos to measurable ROI
Approval rate
15% → 30% consent conversion
Less manual effort
15–20 min → ~2 min per asset
Rights visibility
Centralised lifecycle tracking
My role
What I owned
As Head of UX Design at Woovly India (Live2.ai), I led this project end to end — from discovery research through system design, prototype and stakeholder alignment. I owned the problem framing, the UX architecture, all interaction design and the compliance layer. I worked directly with enterprise clients including Meesho, Schwarzkopf and Rare Rabbit to validate pain points, and partnered with engineering and legal to ship within platform constraints.
This was not a UI redesign. It was a system design problem masquerading as one — and identifying that distinction was the first design decision I had to make.
Business context
The UGC explosion created an operational bottleneck
Live2.ai enables brands to fetch, curate and distribute user-generated content at scale. By 2024 the platform was automating the first two steps — discovery and curation. But every campaign was stalling at the same point: getting legal permission to actually use the content.
"Manual DM-ing is a logistical nightmare. We need a 50-person team just to copy-paste legal terms."
For high-stakes global brands like Schwarzkopf and Swisse, the risk was different but equally paralysing. Legal teams were blocking content use entirely because there was no provable, timestamped record of creator consent.
"One unlicensed photo on our site could lead to a multi-million dollar lawsuit."
Great UGC was sitting unused — not because brands didn't want it, but because there was no safe, scalable path from "found it" to "cleared to publish".
Discovery
Three research inputs, three convergent findings
I ran discovery through brand marketing team interviews, campaign manager feedback sessions, support ticket analysis and an audit of existing operational workflows. Instagram's platform API documentation was also a primary input — not just for engineering context, but to understand what any solution could realistically automate.
Finding 01
Rights requests happen at the worst possible time
- Brands discover high-value UGC during active campaigns
- Manual rights process delays activation by days
- Content loses freshness before it can be published
Finding 02
Manual outreach doesn't scale past ~20 posts
- Meesho collects 1,500+ UGC posts weekly
- Individual DM outreach requires a 50-person team
- Manual effort eliminates the ROI of using UGC
Finding 03
Platform APIs restrict automation by default
- Instagram API only works when the brand is tagged
- Untagged posts — often the best UGC — have no API path
- Each constraint needed its own design response
The status-quo workflow, mapped from observation
Before
- Find post
- Verify fit
- Draft DM
- Send DM / email
- Wait for reply
- Screenshot / copy
- Log in Excel
Average time to license one asset: 15–20 minutes
Problem definition
Rights at scale is a system problem, not a UI problem
The instinct is to reach for a better form or a bulk-send button. Reframing the problem was the most important design decision I made: the challenge wasn't UI — it was managing a lifecycle under several enforcement boundaries at once.
Platform
API restrictions
Automated comments and DMs only work when the brand is tagged. No API path for untagged posts.
Automation
Trust limits
~200 automated DMs/hr for professional accounts, 20–50/day for new ones. Exceeding them risks platform penalties.
Legal
Compliance
Must store timestamped, verifiable proof of consent, with specific approval language and T&C links.
The problem statement I used to align the team
"Enterprise brands acquiring high volumes of UGC need a scalable, compliant way to request and manage usage rights — without violating platform rules, exceeding automation limits, increasing manual workload, or losing legal traceability."
Design decisions
Four interconnected decisions that made the system work
01
Template-based legal messaging with an embedded approval trigger
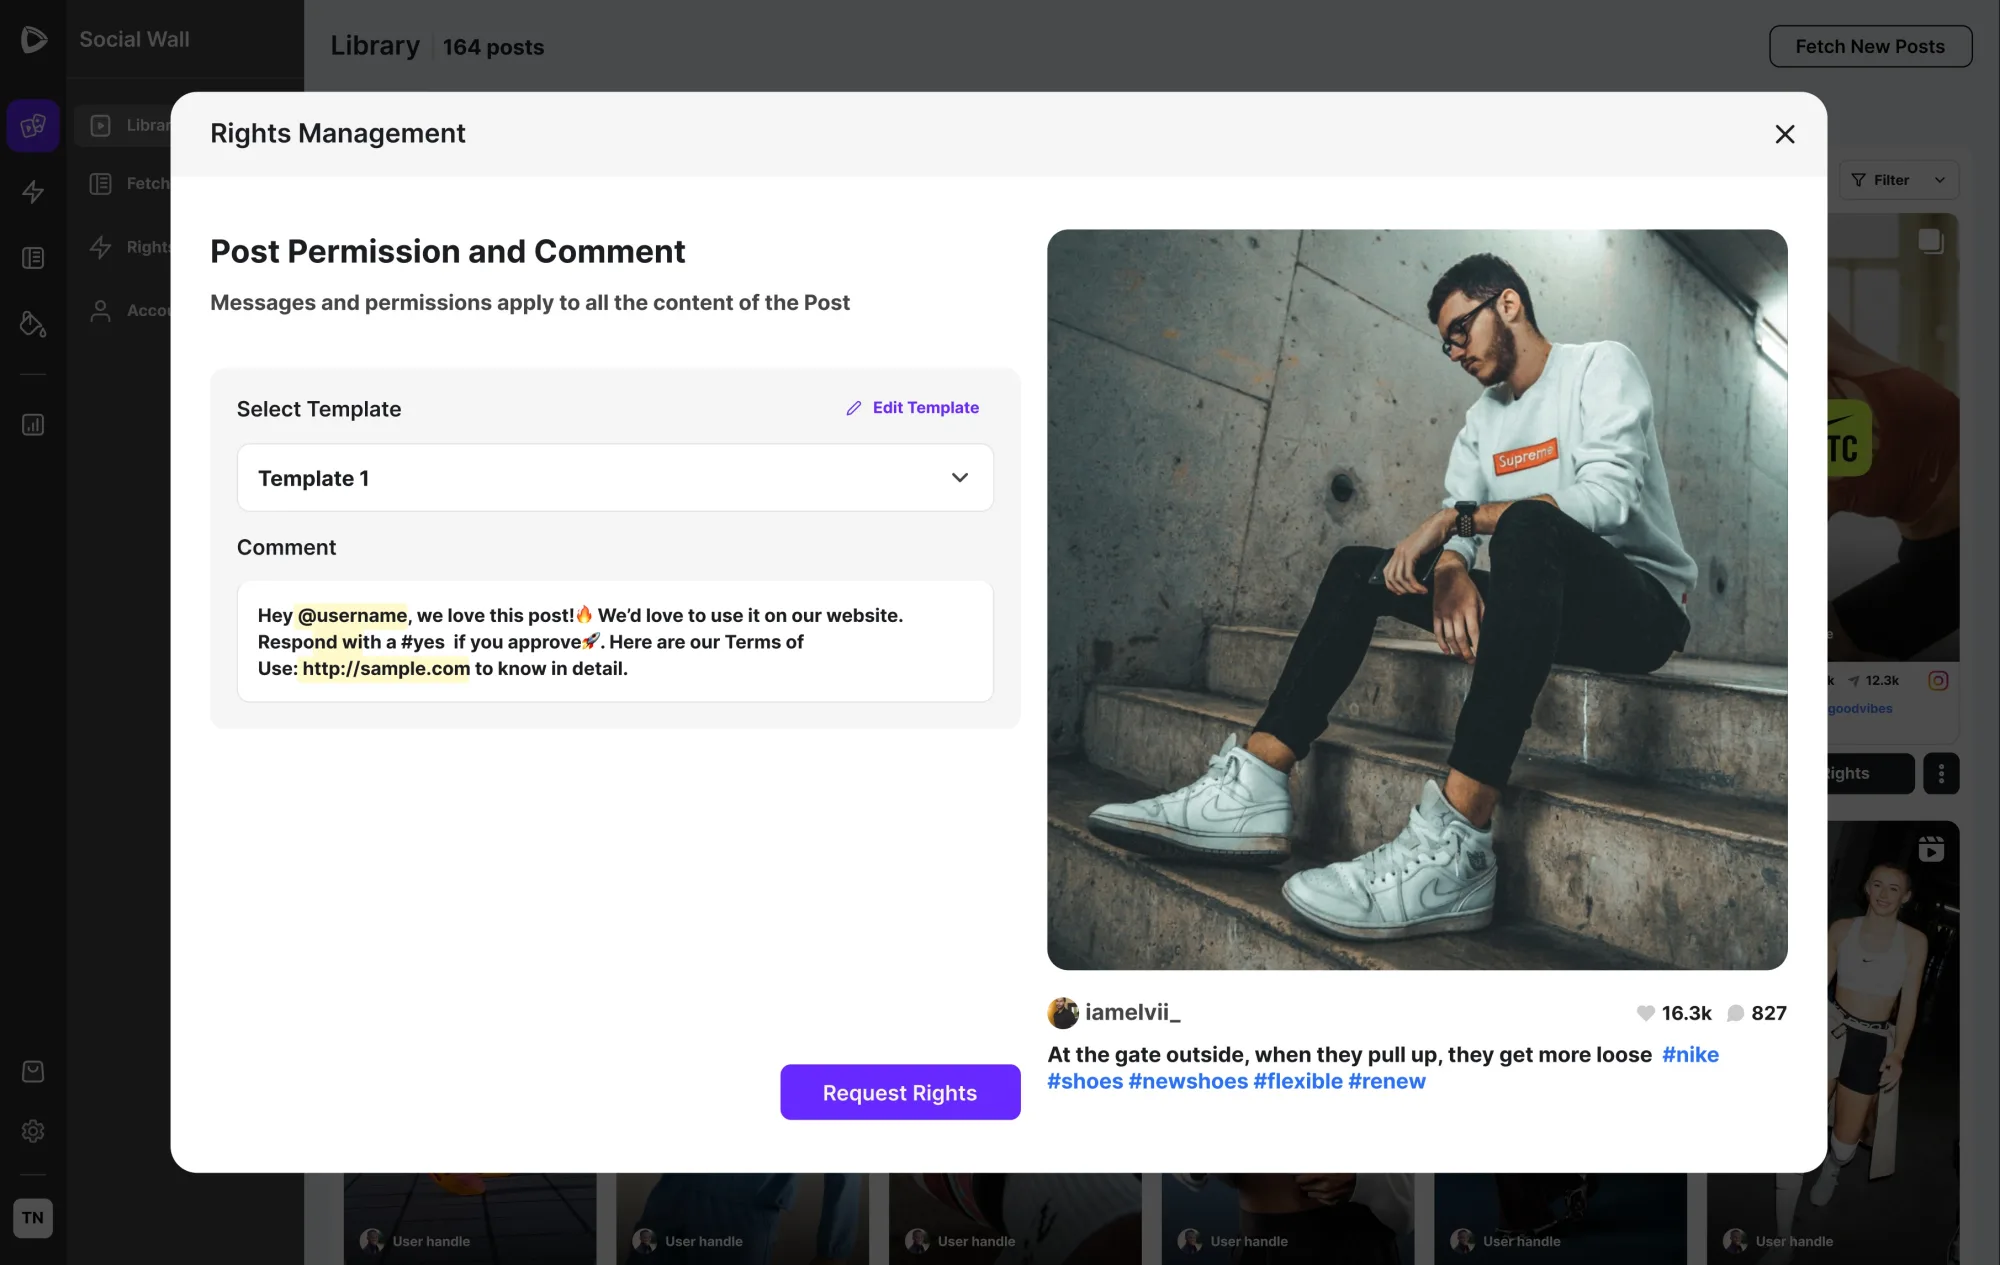
Instead of free-text DMs, I designed a template system with pre-approved legal language and a structured keyword trigger (#yes). Approval is only recorded when this keyword is detected via the API — no ambiguous replies, no manual interpretation.
Why not free-text DMs
A creator replying "sure 👍" or "go ahead!" isn't verifiable consent. A keyword trigger is automatable, unambiguous, and creates a legal record.
02
Graceful no-tag fallback with full lifecycle continuity
When Instagram's API blocks automated commenting (brand not tagged), the system detects it up front and offers a one-click manual recovery path: the compliant comment is copied to the clipboard, the creator's post opens directly, and the outreach is logged in the same tracker as automated requests. No silent failures. No workflow exits.
Why it matters
Untagged organic posts are often the highest-quality UGC. A broken flow here would force brands to abandon their best content or keep a parallel spreadsheet — defeating the product's core value.
03
Rate-aware smart queuing with visible status
Selecting 300+ posts doesn't fire 300 simultaneous API calls. The system tracks the brand account's hourly and daily DM budget, sends within safe thresholds, and queues the rest with a clear "Scheduled" status. Users see progress, not mystery.
Why not plain bulk-send
Hitting Instagram's limits doesn't just pause outreach — it damages the account's trust score and can trigger restrictions on all future automation. Long-term account safety had to be a design constraint, not an afterthought.
04
Versioned T&C templates with a full audit trail
Legal teams need to prove not just that consent was given, but which version of the terms was active at that moment. The system stores T&C version history, timestamps each version, and records which one was attached to every rights request.
Why it matters
Enterprise legal teams were the main reason great UGC sat unused. This unlocked content previously blocked by compliance — where the largest business value was concentrated.
Prototype flows
Three flows that prove the system
Rather than every screen, these flows show the core decisions in context: the end-to-end journey from content to consent, the no-tag recovery, and the centralised dashboard.
Flow 01
End-to-end rights request journey
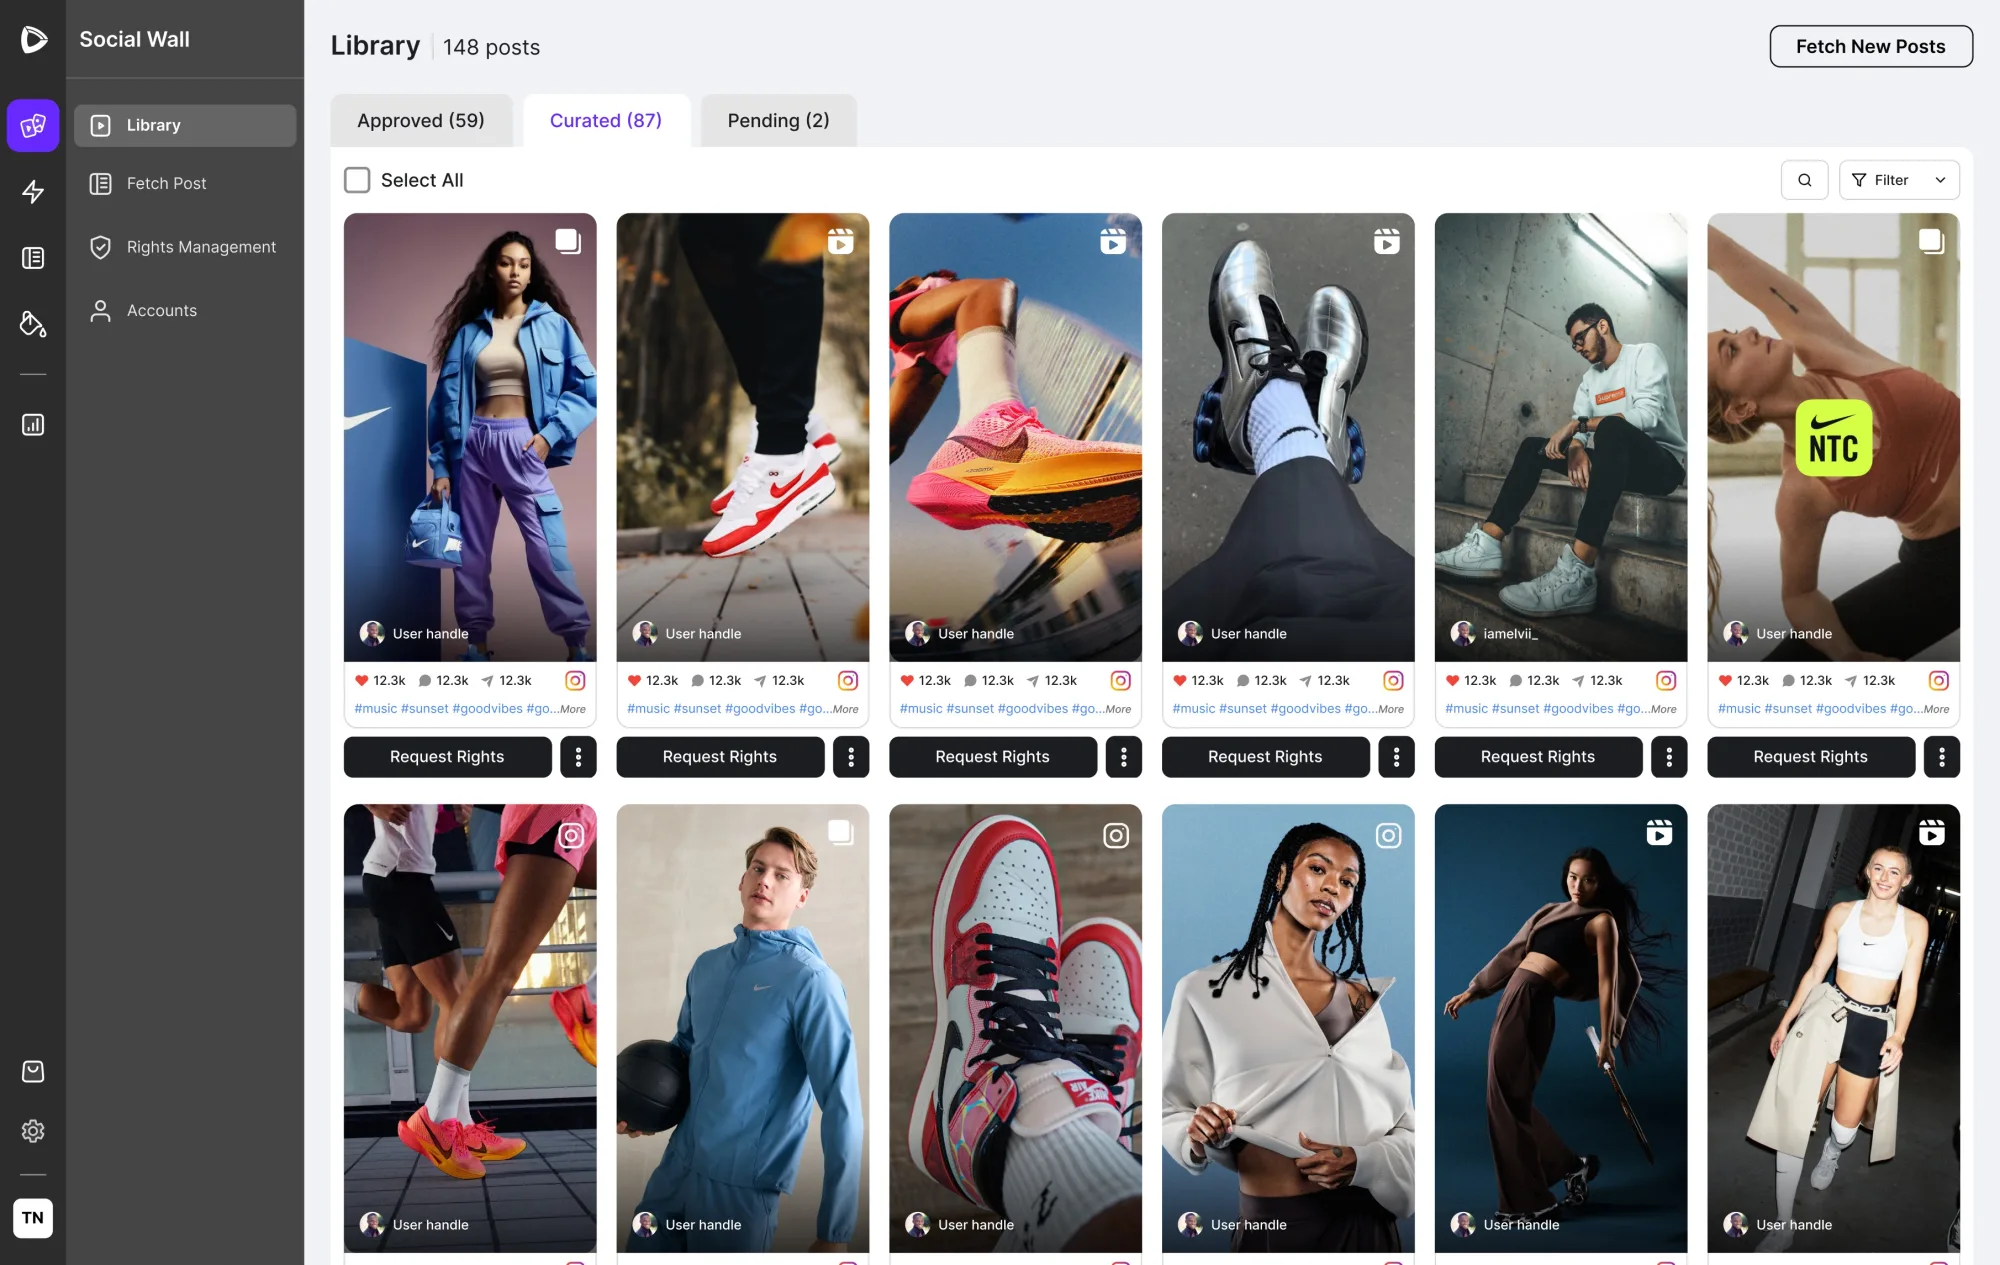
From browsing the curated library to a verified, timestamped creator approval on Instagram.
Design decision
Engagement metrics surface before the marketer commits to requesting rights — preventing wasted outreach on low-value content. Multi-select enables bulk requests while each post's context stays visible.
Design decision
The live post preview stays beside the form, confirming the right asset is being requested. The template enforces legal language; the #yes keyword enables automated consent detection without manual review.
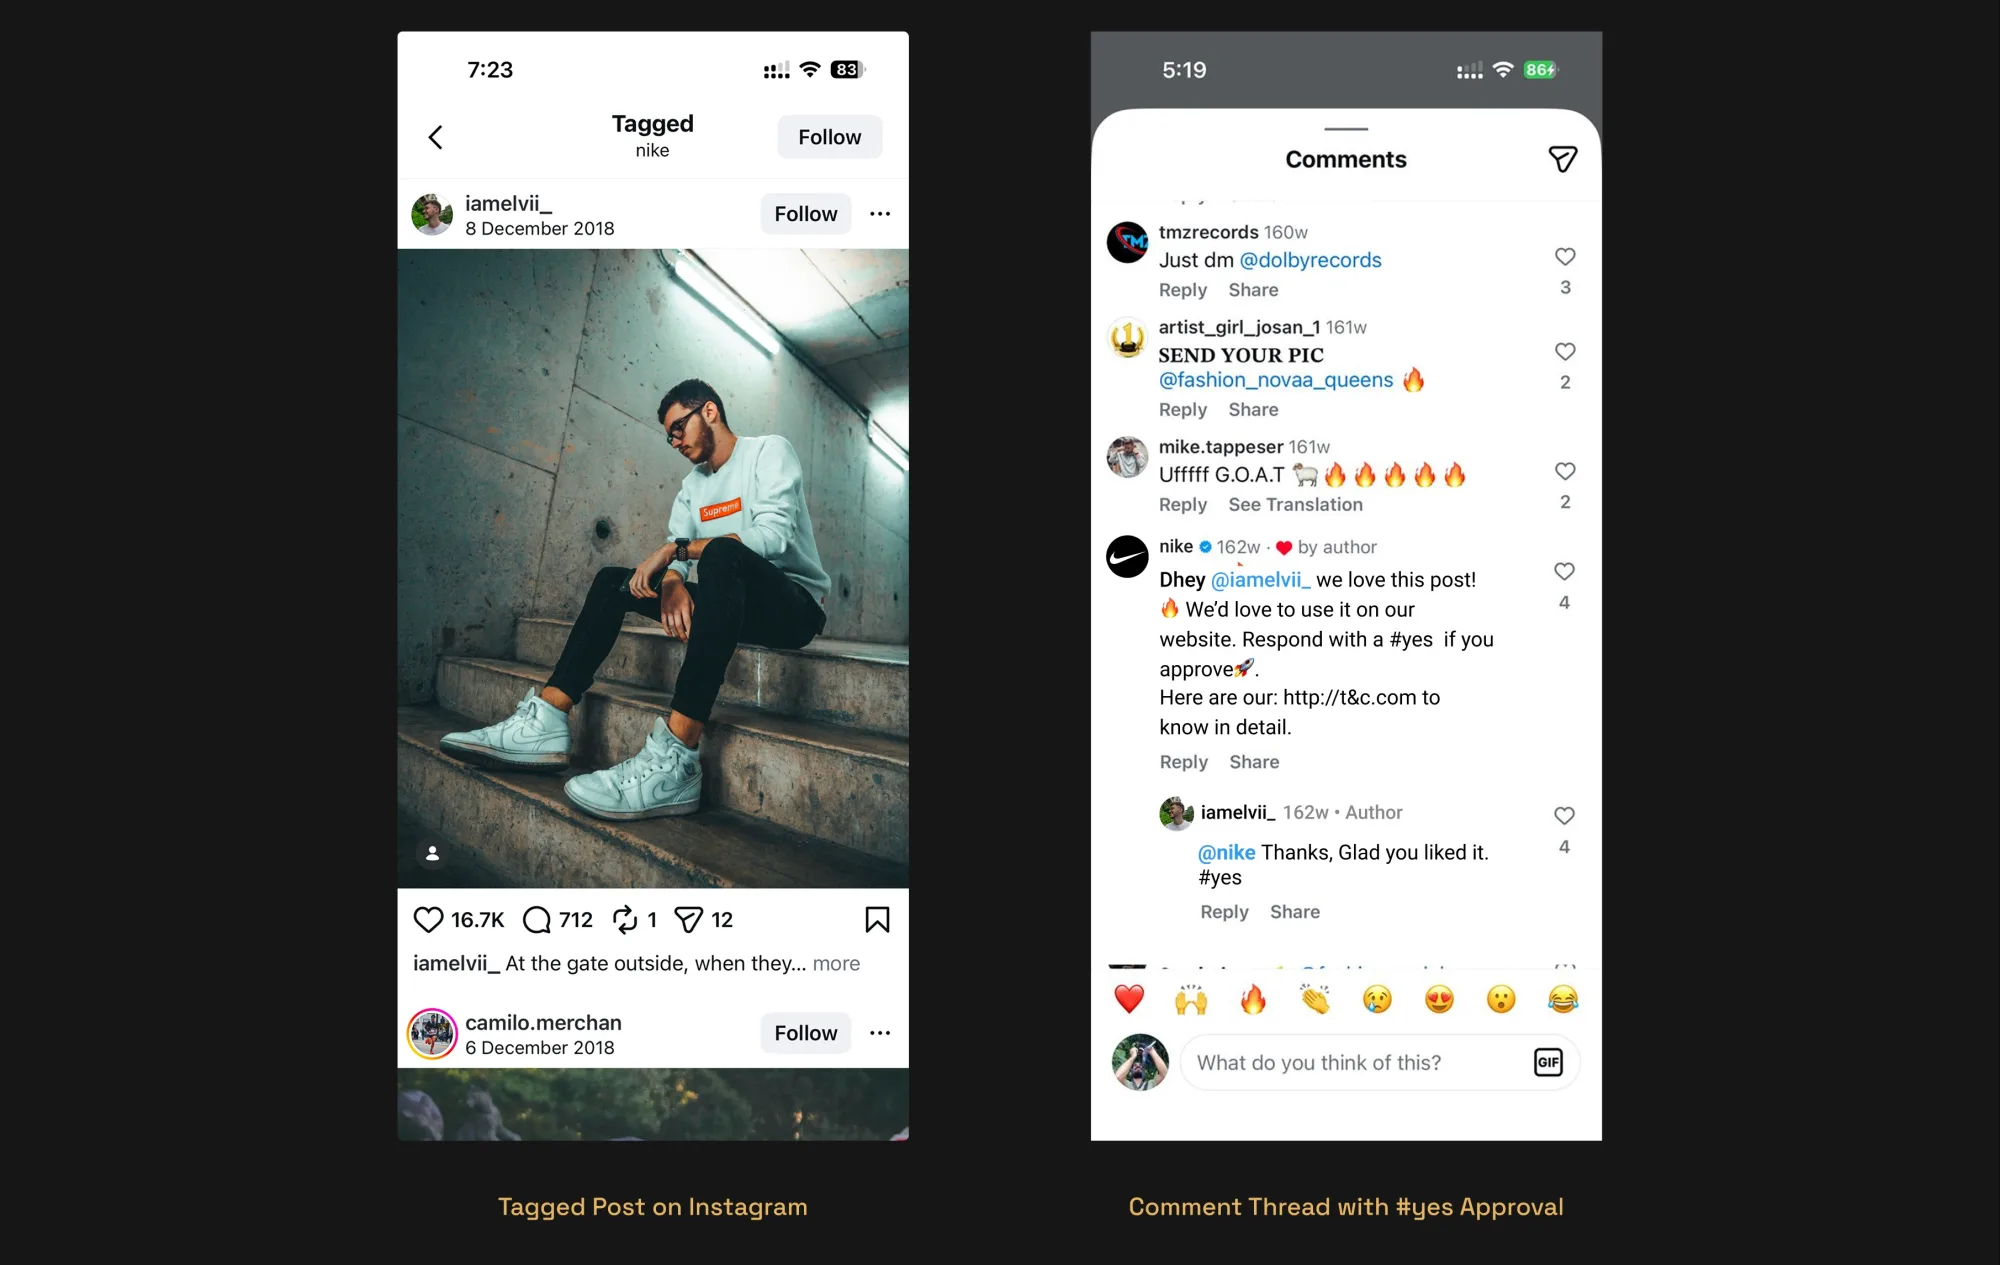
How consent is captured
The system monitors for #yes via the Instagram API. When detected, the timestamp is recorded, the creator's message stored and the status moves to Approved — no manual review. This is the legal proof of record.
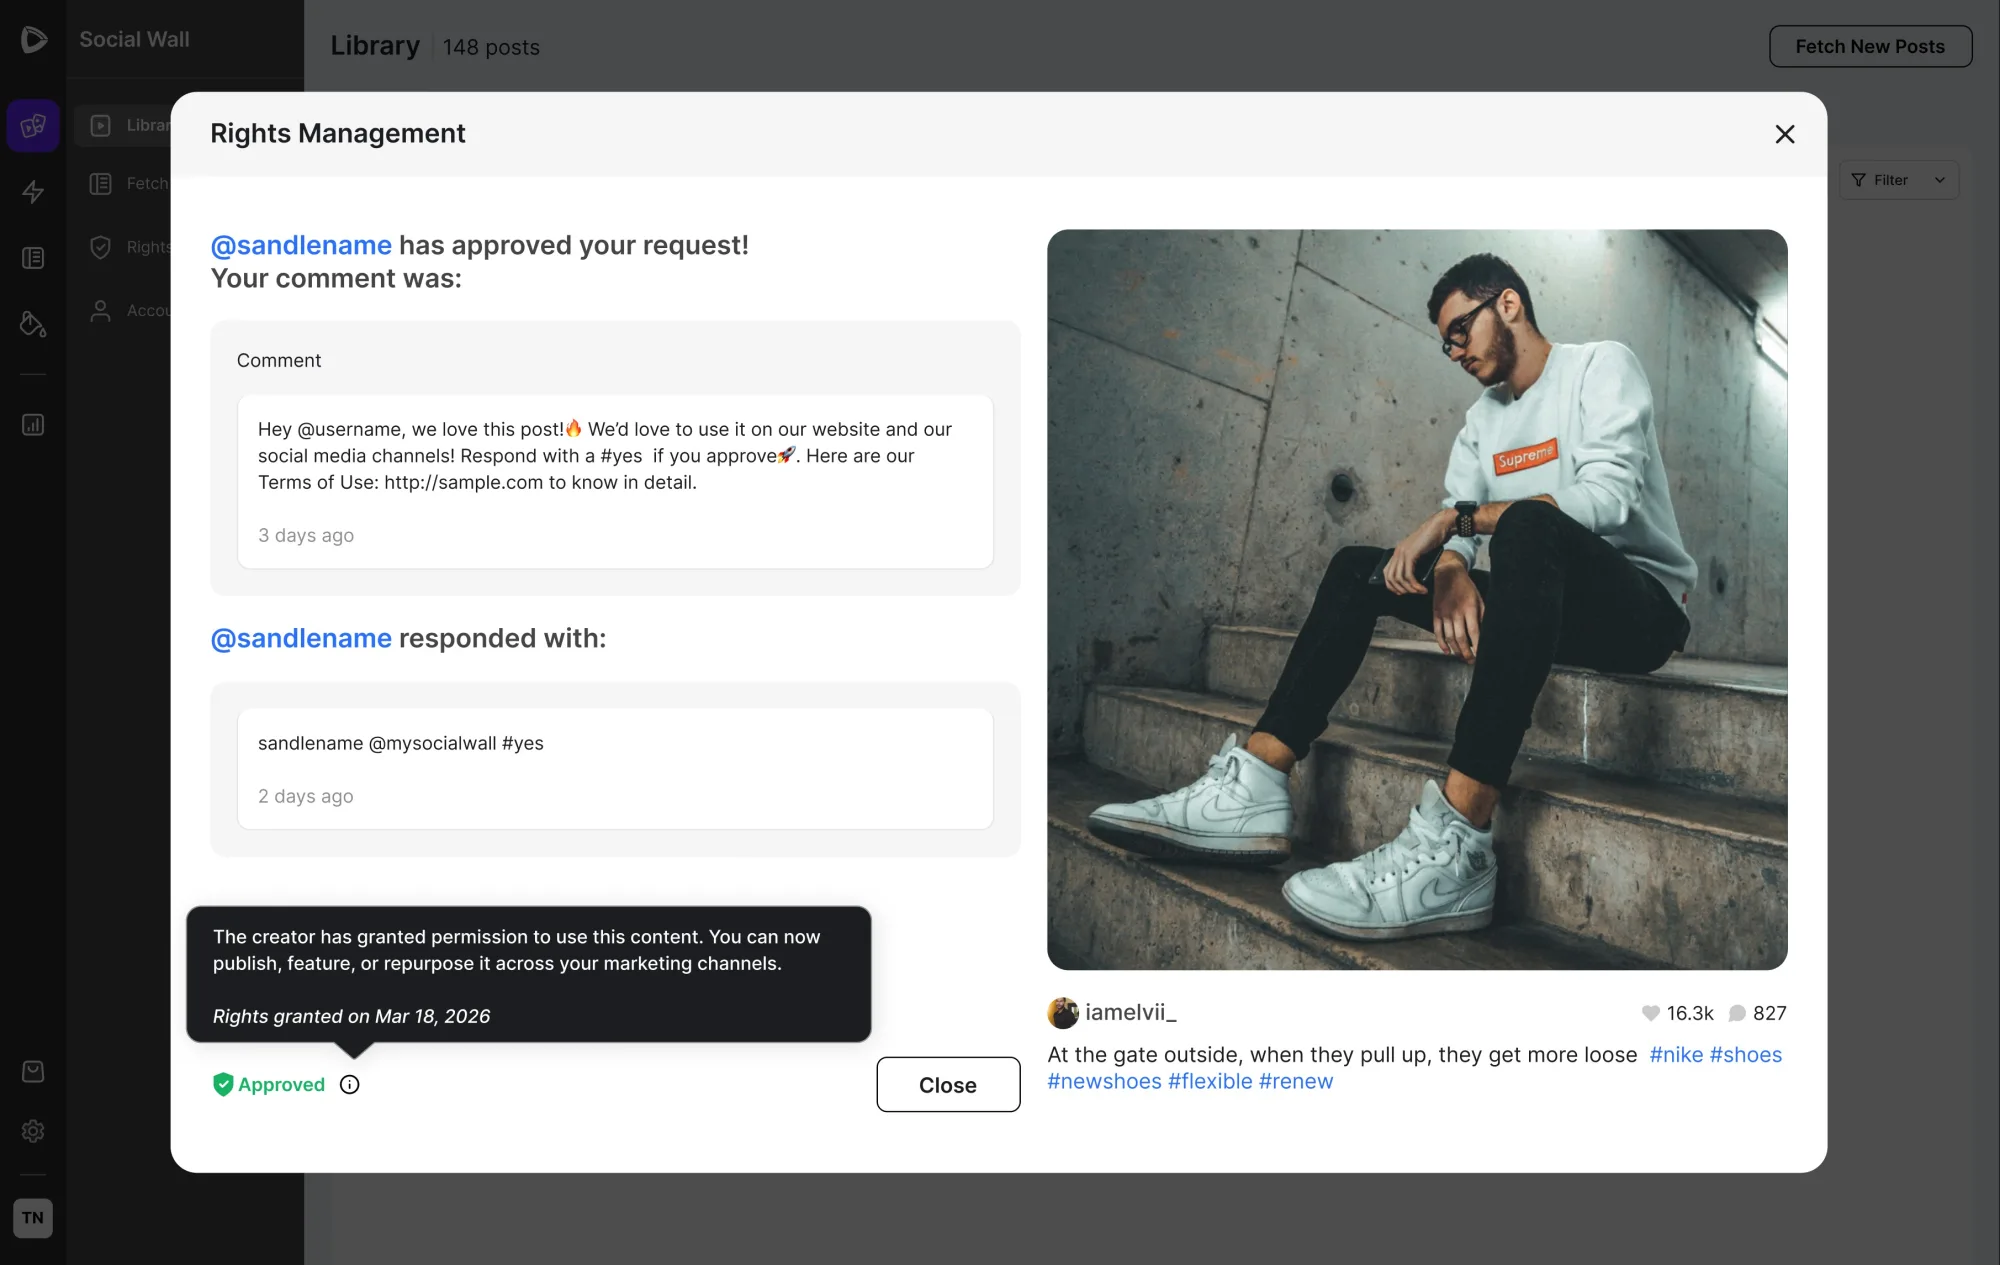
Design decision
Every outreach appears in one list with the same status vocabulary. The approval record stores template, channel and T&C version — so the legal proof is always attached to the content, not in a separate system.
Flow 02 · Key design decision
The no-tag fallback
When the brand isn't tagged, Instagram blocks automation. Instead of failing silently, the system routes to a compliant manual path with full lifecycle continuity.
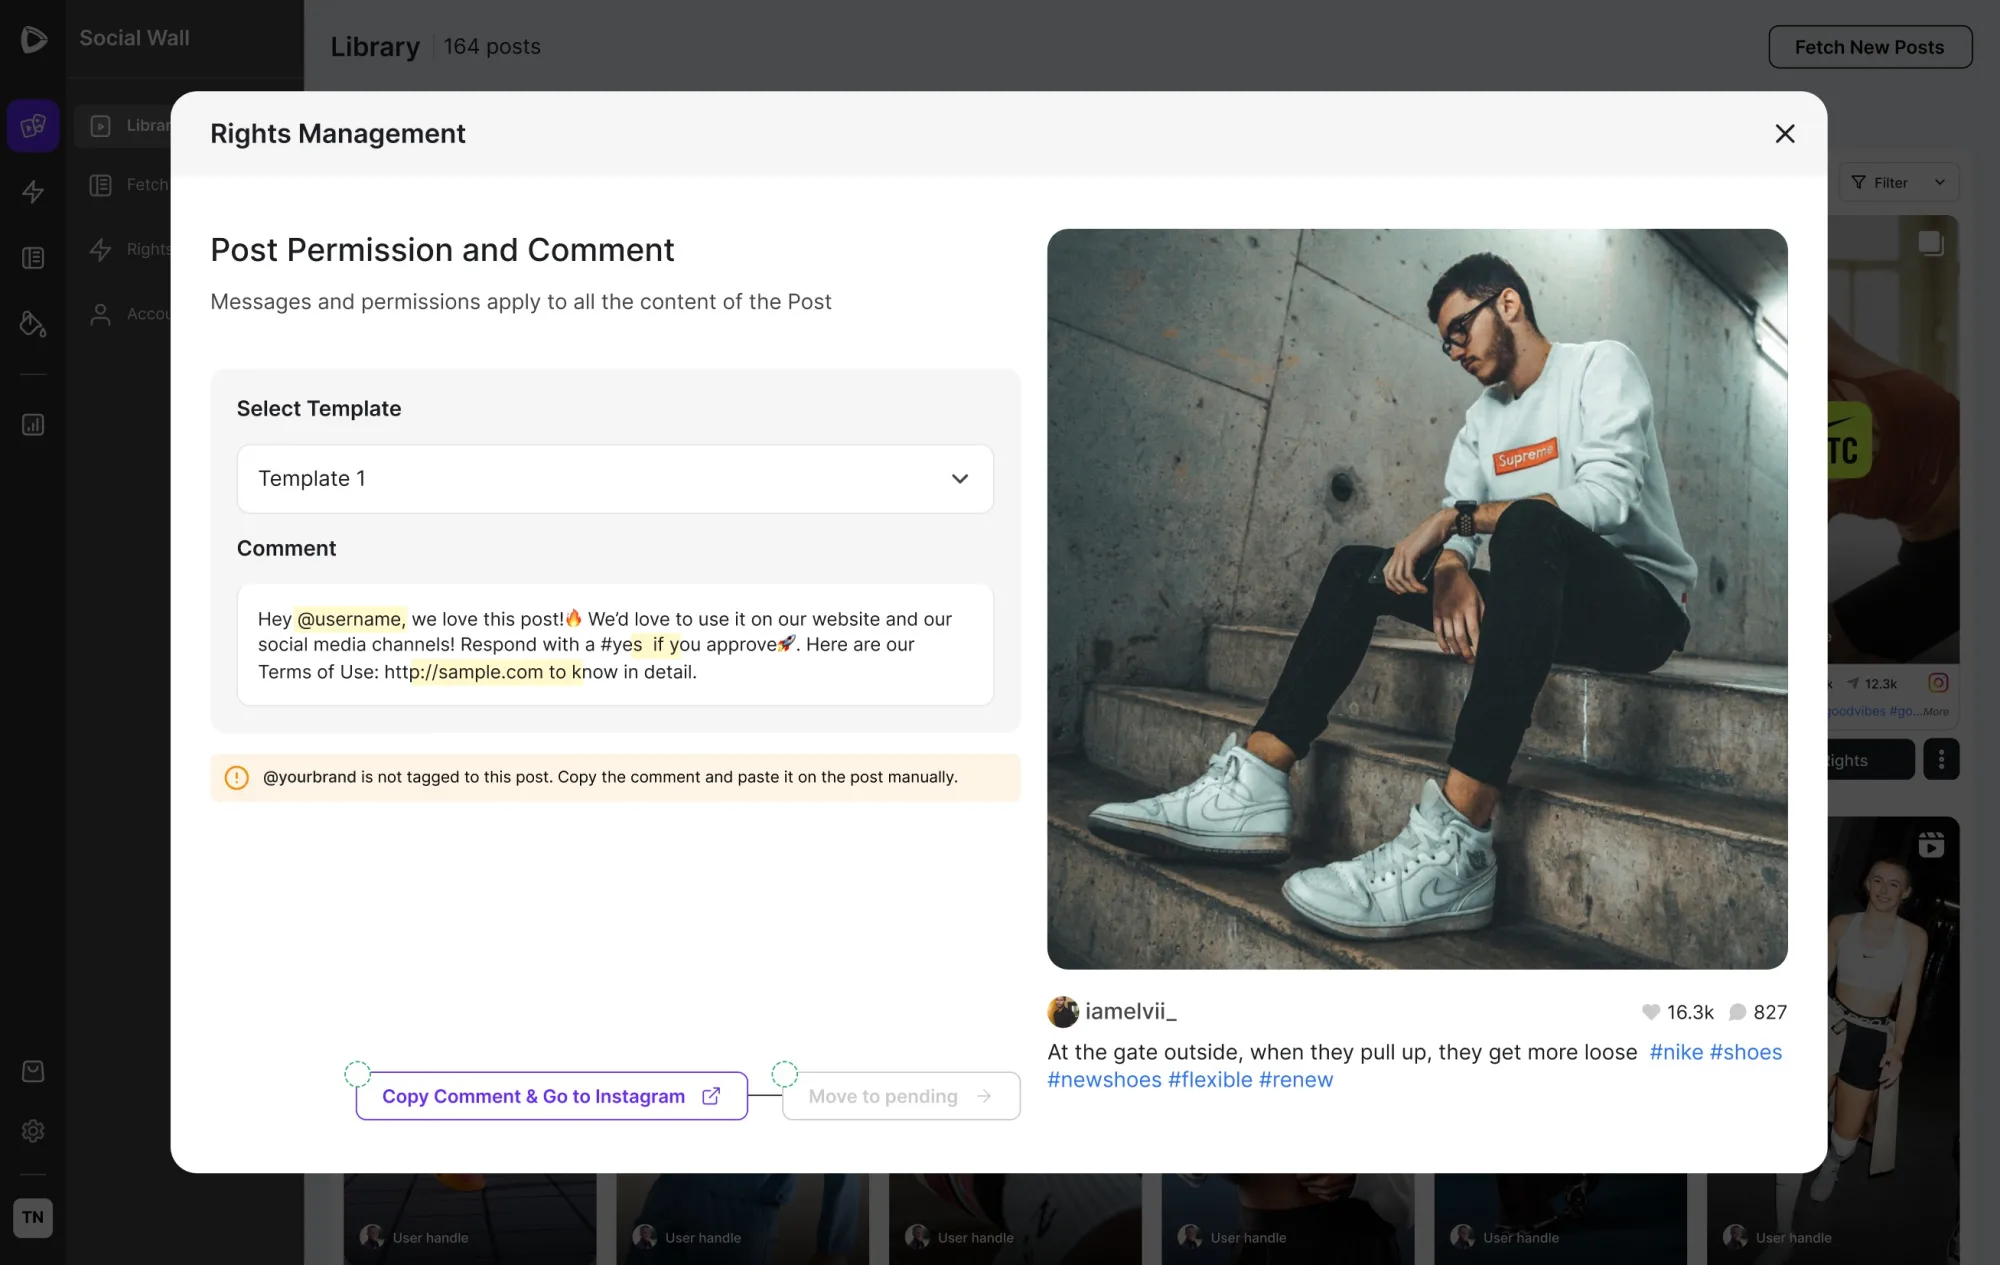
Why not fail silently?
A silent failure leaves the marketer confused and the post abandoned. The explicit warning names the constraint, provides the compliant message pre-written, and offers a single recovery action.
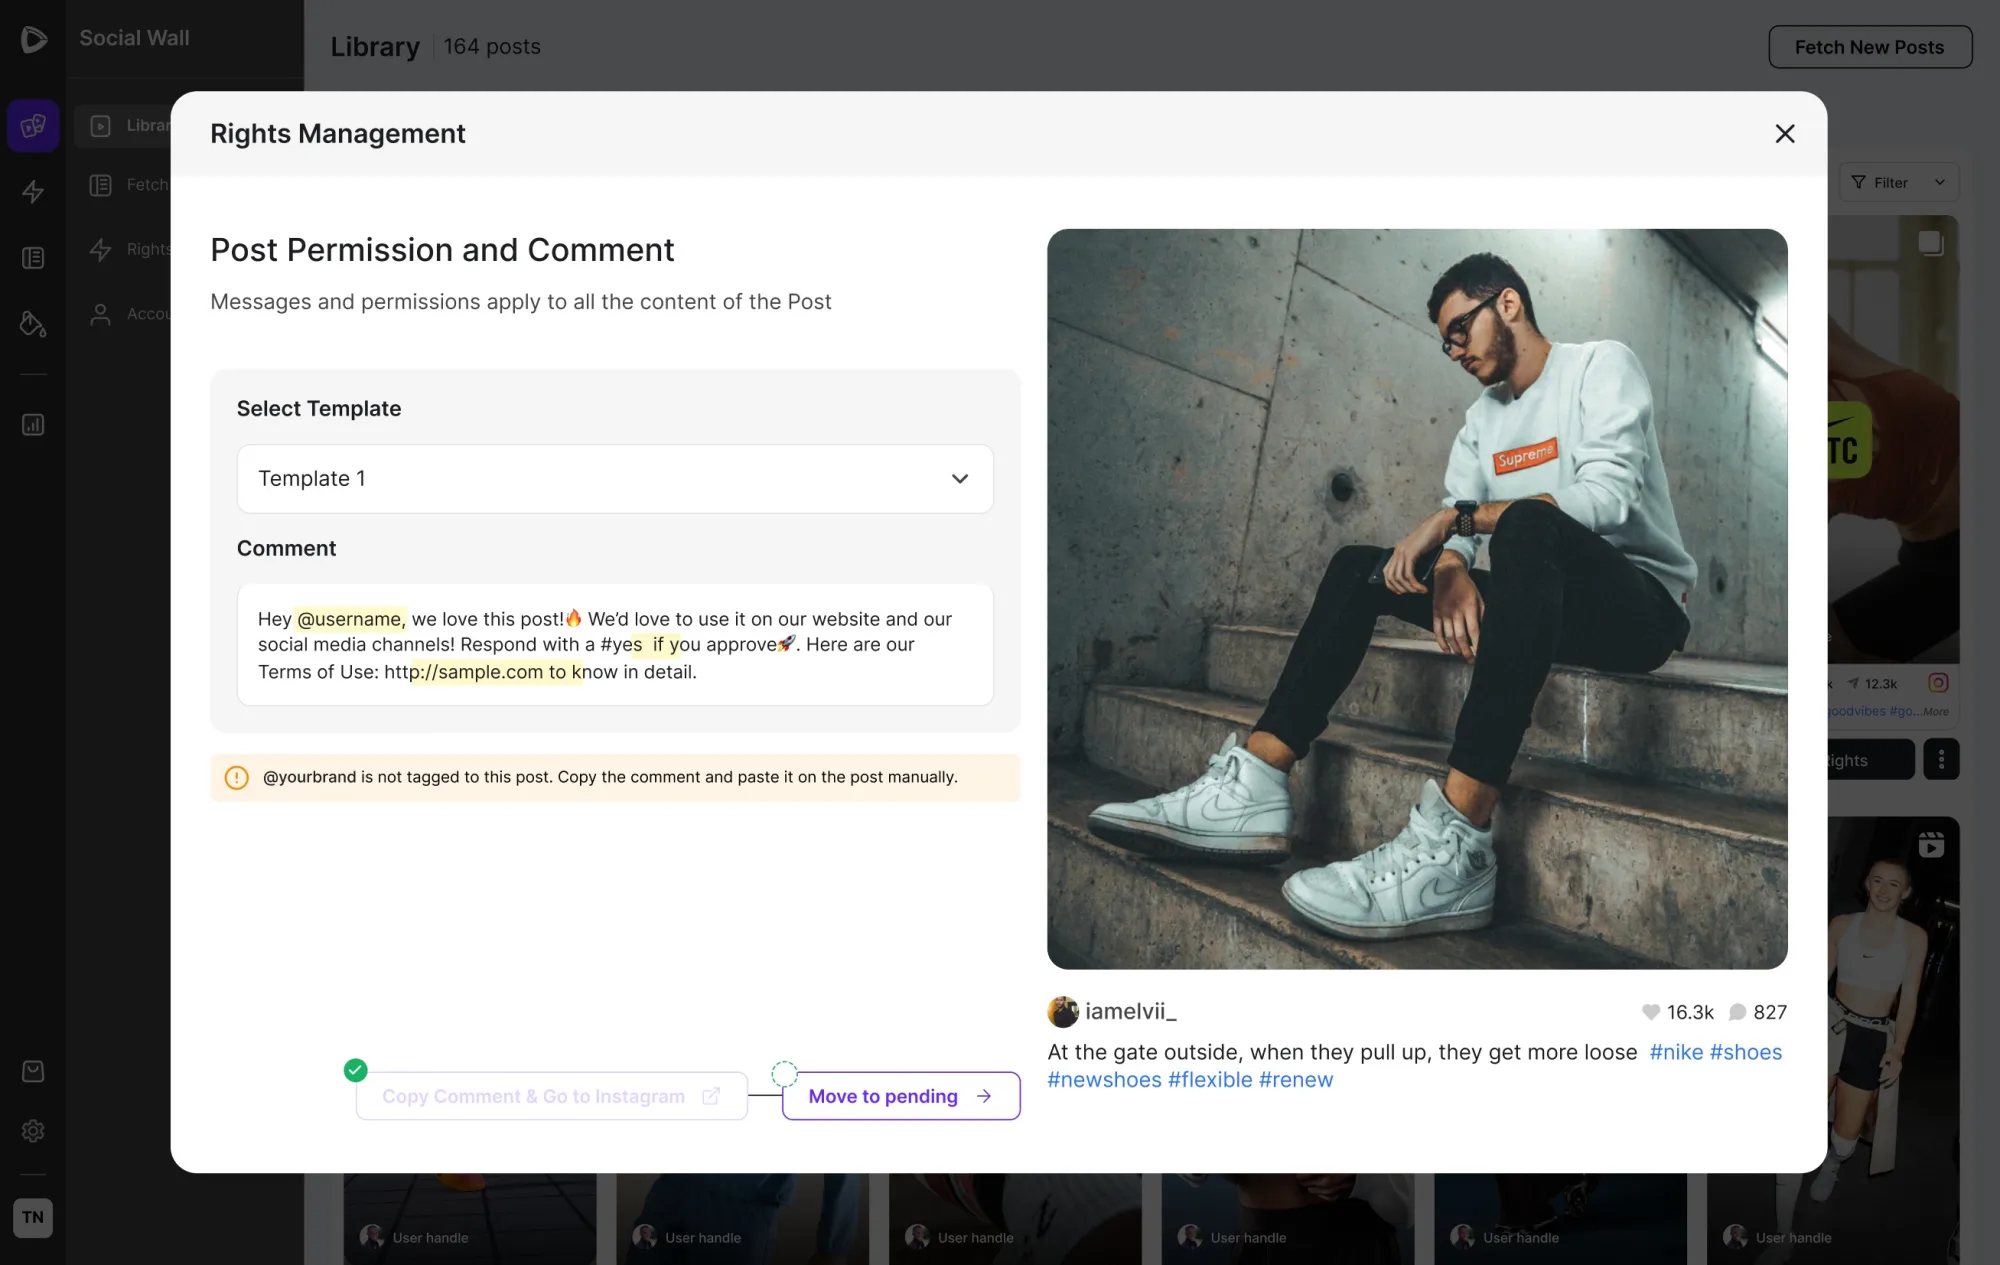
Design decision
Once copied, the call to action shifts to "Move to pending" — the next logical step. Legal language, the #yes keyword and the T&C link stay exactly as in the automated flow.
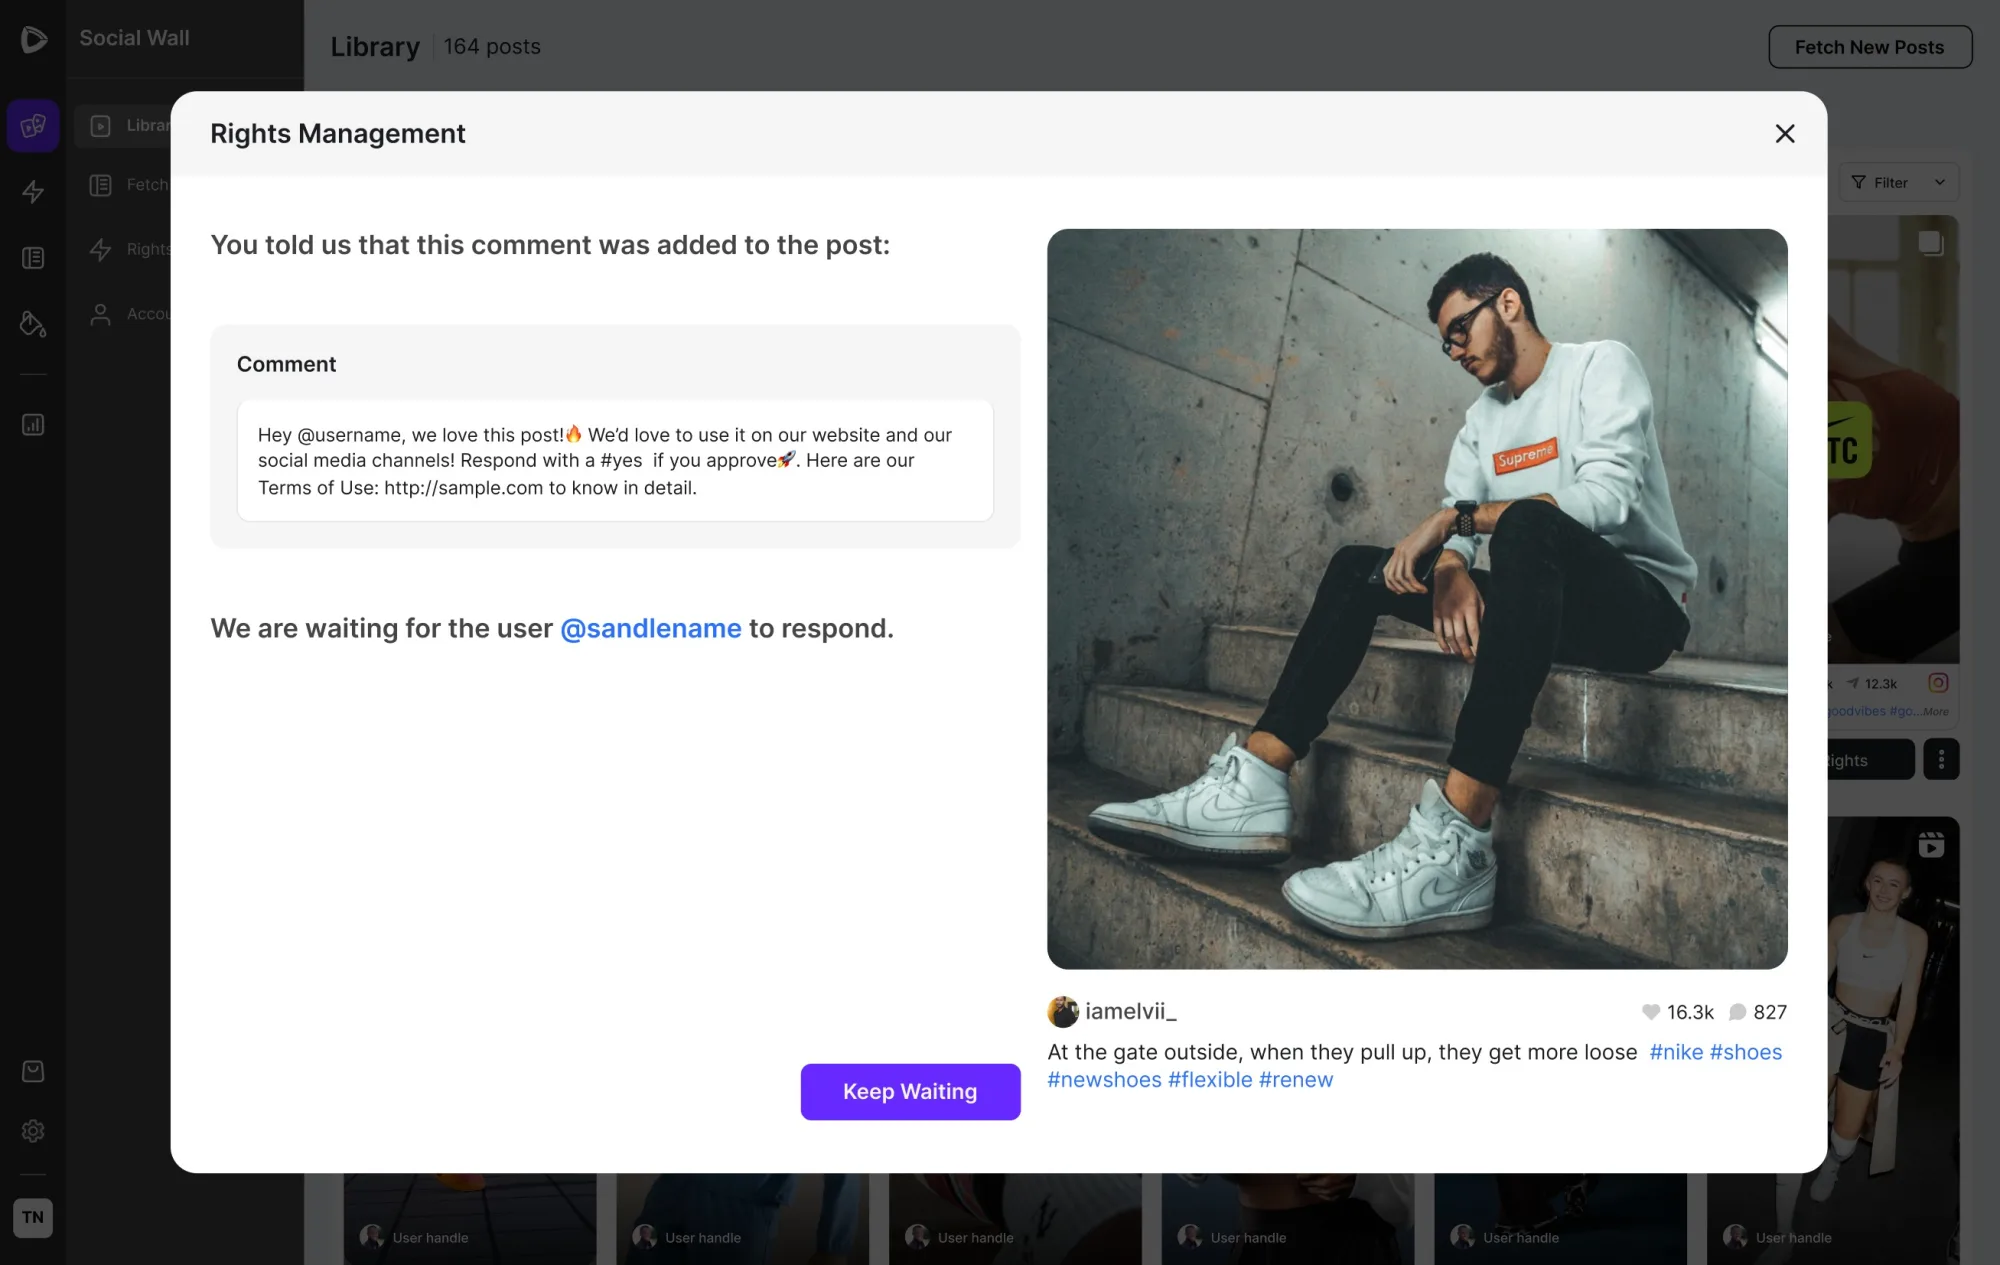
Lifecycle continuity
Manual and automated outreach share identical states. No separate spreadsheet — everything is tracked in one place with a full audit trail, however the outreach started.
Flow 03
Centralised rights dashboard
The dashboard that replaced spreadsheets — rights tracker, versioned message templates with conversion data, and T&C history for legal audit.
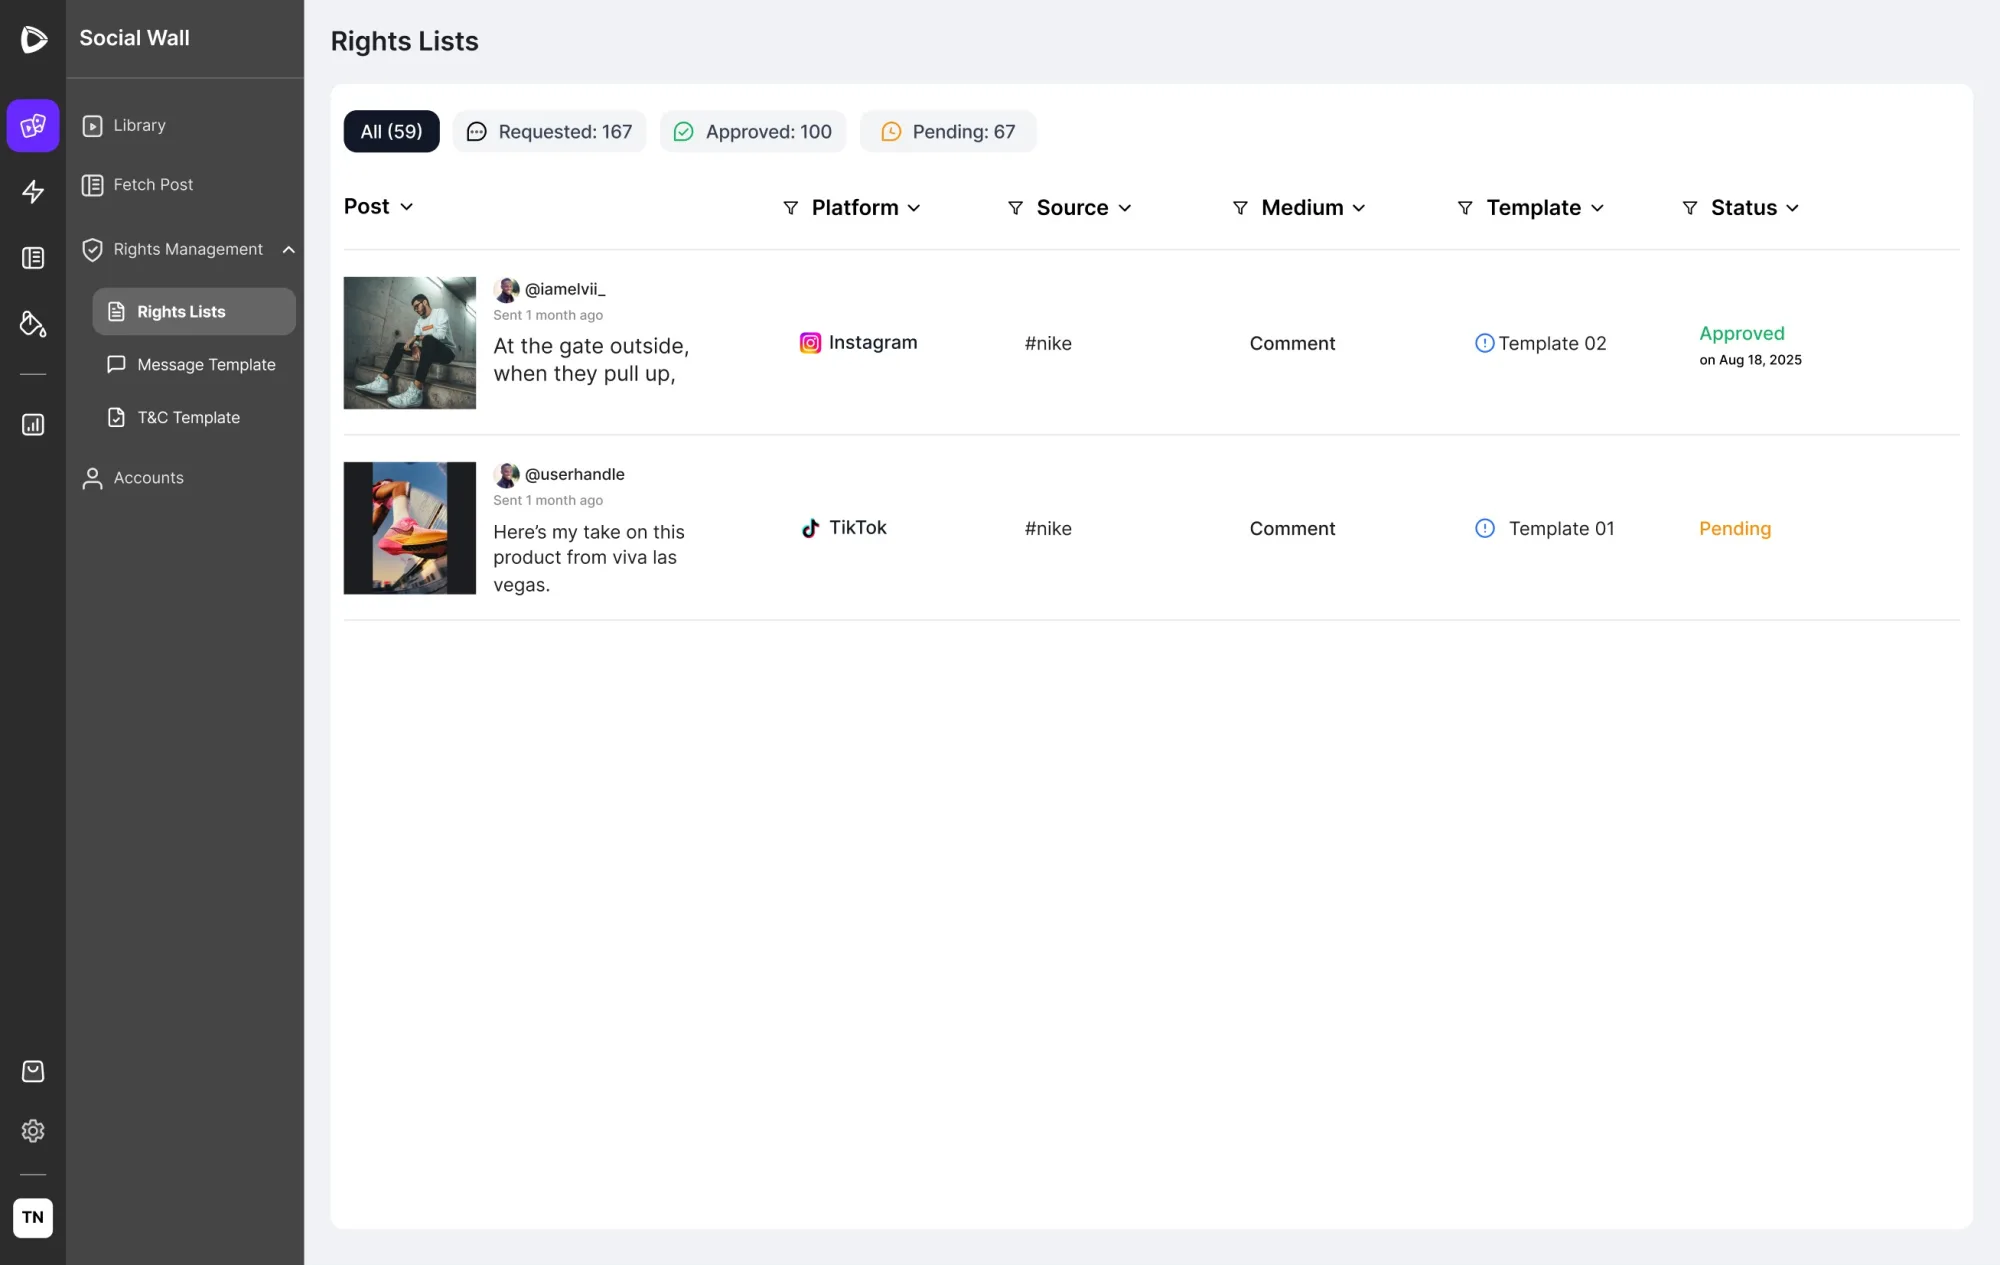
Design decision
Template and channel always sit beside status — teams know exactly what was sent and where. Export supports legal reporting.
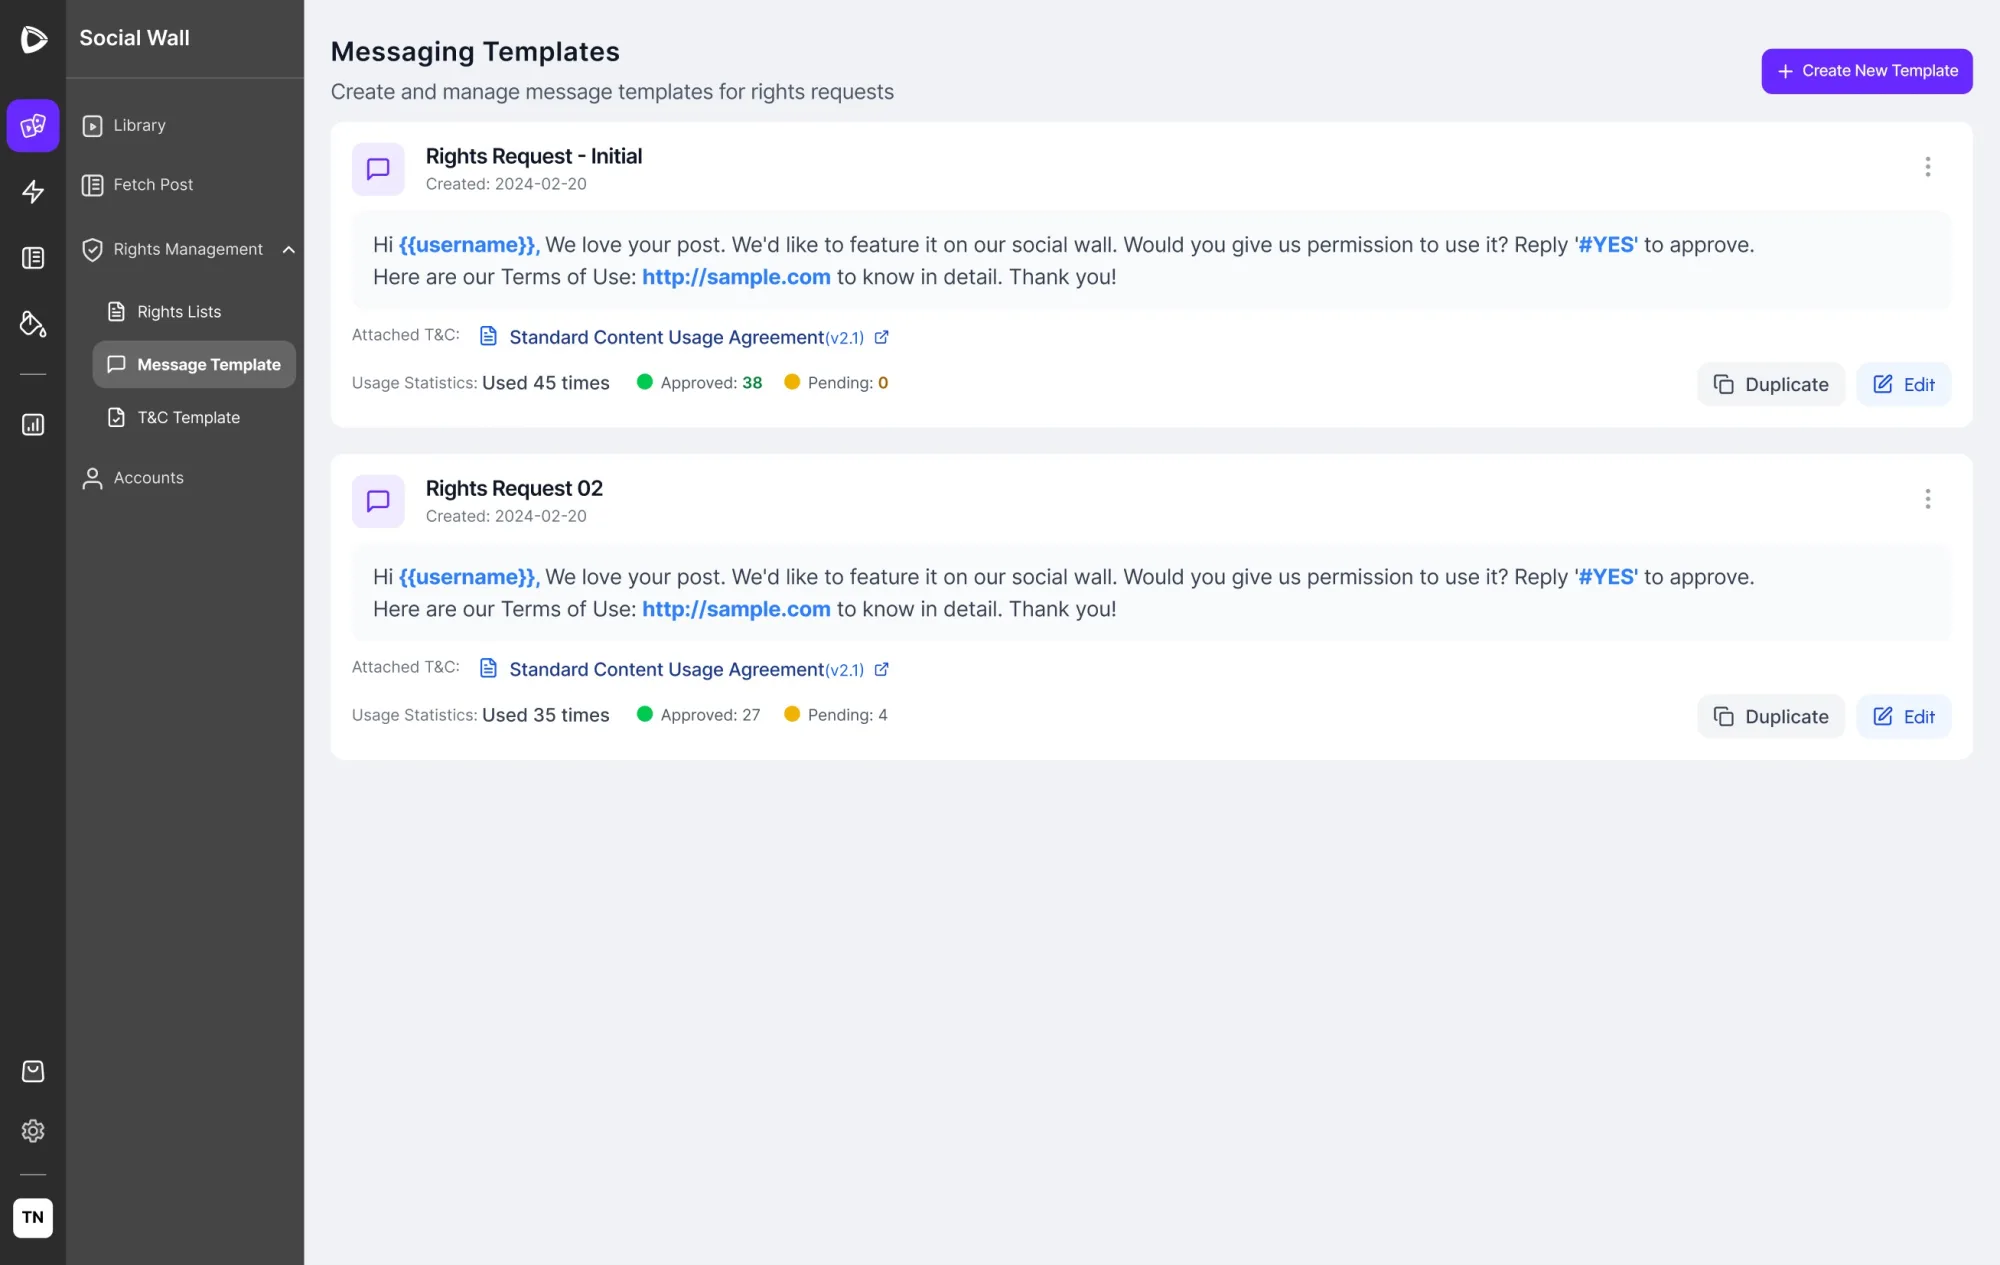
Design decision
Approval rate shows per template, giving teams data to A/B test messaging — directly supporting the 15% → 30% approval goal.
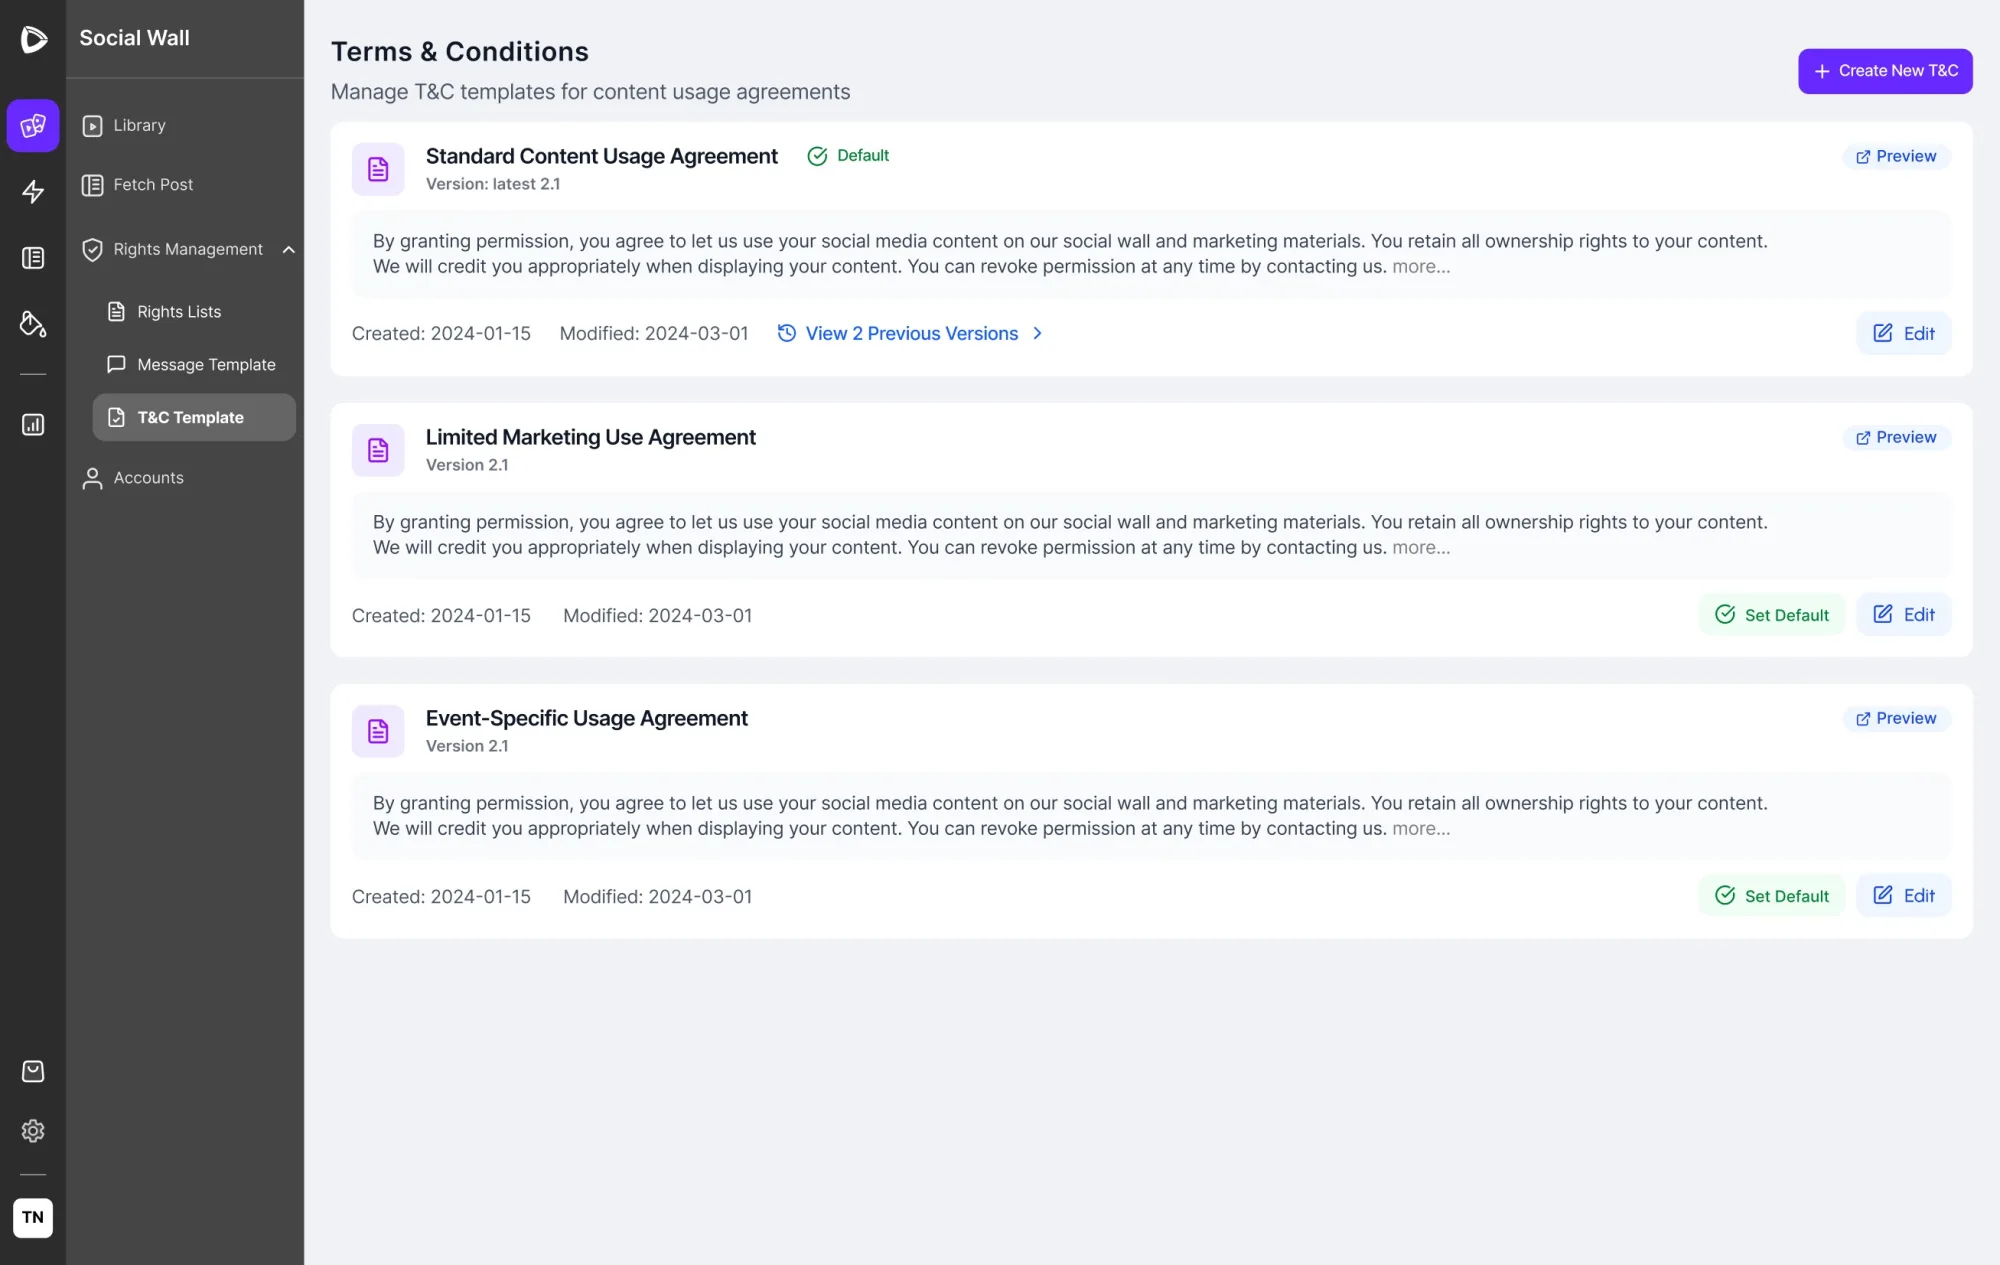
Design decision
If a creator challenges consent, the brand can prove which terms were active at the moment of approval. This was the feature that unlocked sign-off from enterprise legal teams.
System design
A single lifecycle, covering every path
Every asset moves through a defined state machine — whether outreach was automated, manually assisted, or still awaiting a response.
| State | Triggered by | System records | Next action |
|---|---|---|---|
| Curated | Content added to library | Post URL, engagement, source | Request rights |
| Requested | Comment / DM sent (auto or manual) | Timestamp, channel, template version, T&C version | Await creator response |
| Pending (manual) | User copied comment, confirmed post | Manual outreach flag, timestamp | Await #yes keyword |
| Approved | Creator replies with #yes | Response timestamp, approval message, channel | Content unlocked for distribution |
| Queued | Rate-limit threshold reached | Queue position, scheduled send time | Auto-sends when budget is available |
Outcomes
What changed for enterprise clients
Post-launch data showed improvement across the three dimensions that mattered most: legal coverage, operational efficiency and content activation.
Higher consent conversion
15% → 30% approval rate. Structured messaging with clear instructions reduced creator confusion.
Less manual outreach time
15–20 min → ~2 min per asset. Templates, auto-sending and queuing removed copy-paste for tagged posts.
Compliance blocks
Versioned T&C and timestamped approvals gave legal teams the audit trail they needed.
Pipeline visibility
One dashboard tracking every outreach state replaced fragmented spreadsheets.
Reflection
What worked, and what I'd do differently
What worked
- Reframing the problem as a lifecycle system early saved significant rework — the UX only works because the underlying state machine is right.
- The no-tag fallback came from a constraint I first saw as a blocker. Turning platform limits into explicit UX decisions became a signature strength of the system.
- Involving legal as stakeholders, not just reviewers, meant the compliance layer was right the first time instead of bolted on.
- Anchoring alignment in real client pain kept the project from drifting into feature-building.
What I'd do differently
- Build a "compliance-anxious marketer" persona earlier, to sharpen UI decisions around risk tolerance.
- Audit the creator-side experience — how the comment or DM feels to receive could lift consent rates further.
- Design a rejection-handling flow; v1 has no structured way to re-engage a creator who said no.
- Instrument step-by-step funnel data from day one, not just overall approval rate.